

[2024] Pass Microsoft SC-200 Exam Updated 283 Questions
Get 2024 Updated Free Microsoft SC-200 Exam Questions and Answer
NEW QUESTION # 16
You have a Microsoft 365 E5 subscription.
You plan to perform cross-domain investigations by using Microsoft 365 Defender.
You need to create an advanced hunting query to identify devices affected by a malicious email attachment.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.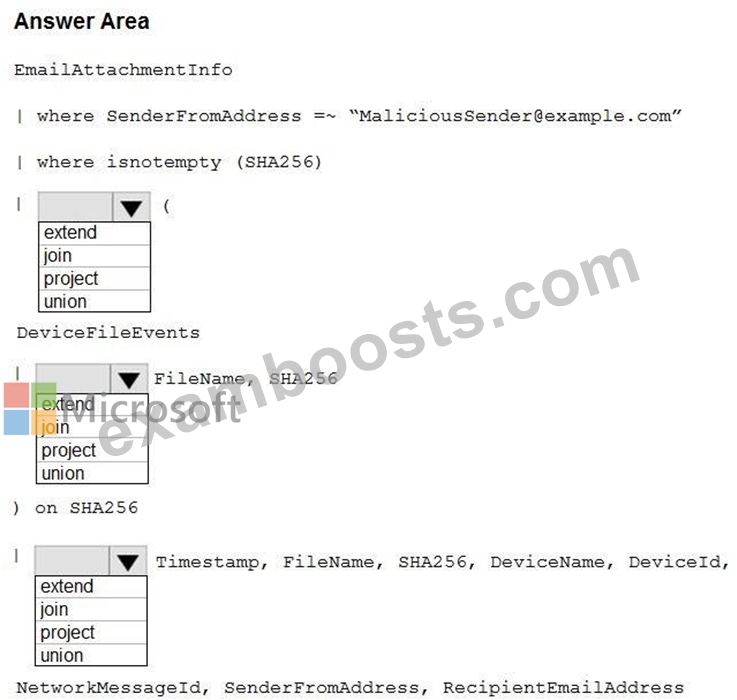
Answer:
Explanation: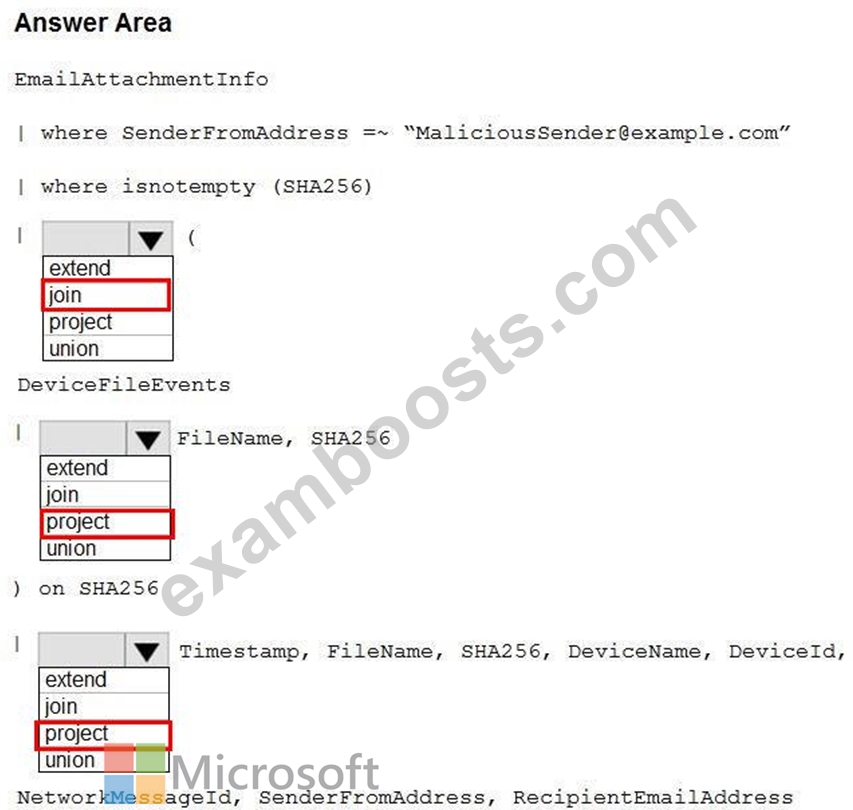
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/mtp/advanced-hunting-query-emails-devices?view=o365-worldwide
NEW QUESTION # 17
You manage the security posture of an Azure subscription that contains two virtual machines name vm1 and vm2.
The secure score in Azure Security Center is shown in the Security Center exhibit. (Click the Security Center tab.)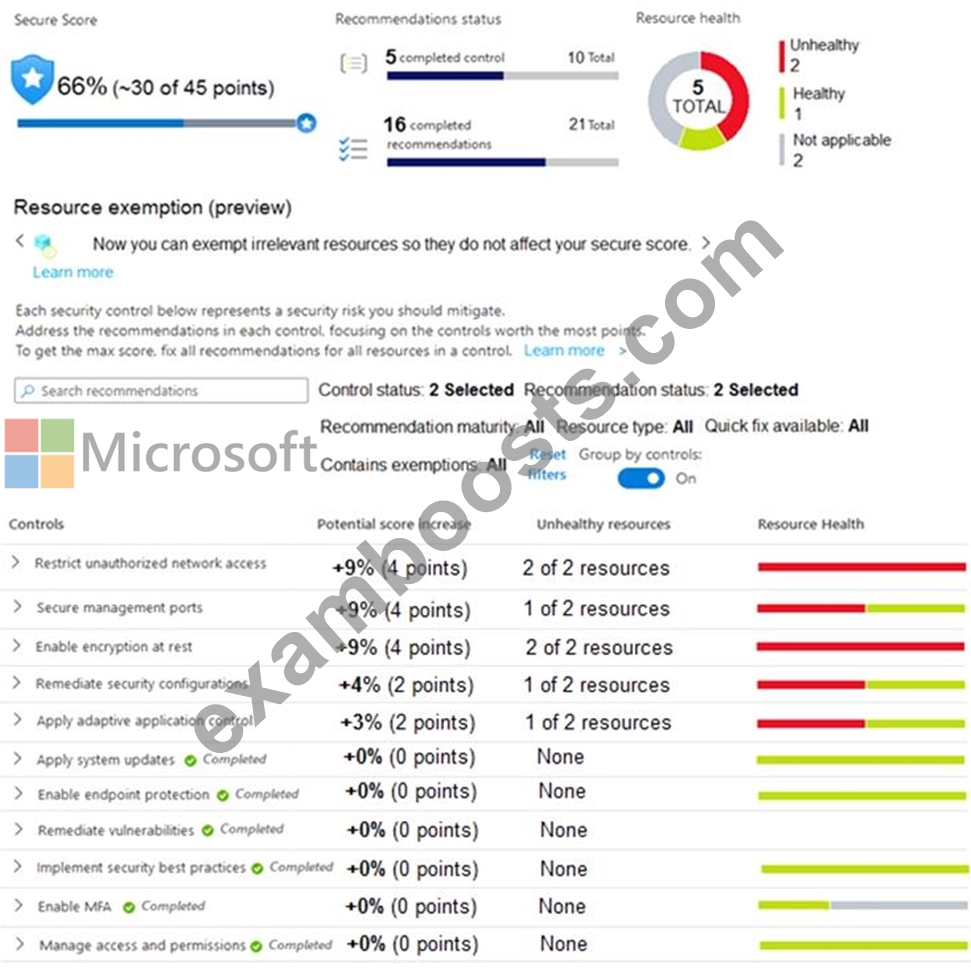
Azure Policy assignments are configured as shown in the Policies exhibit. (Click the Policies tab.)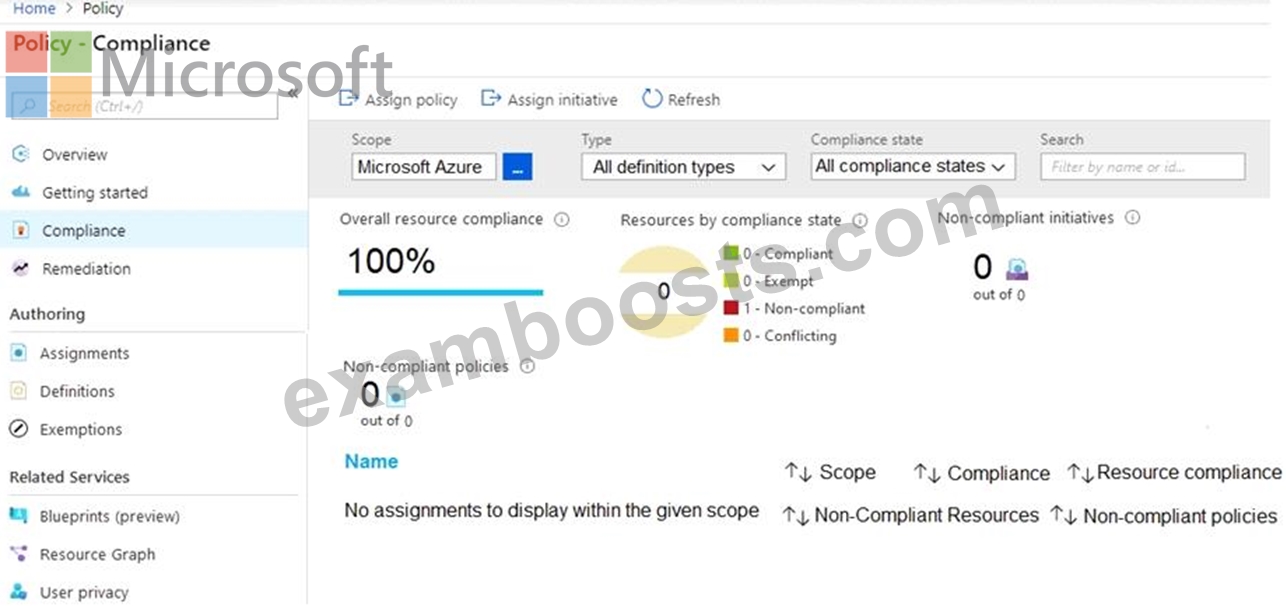
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.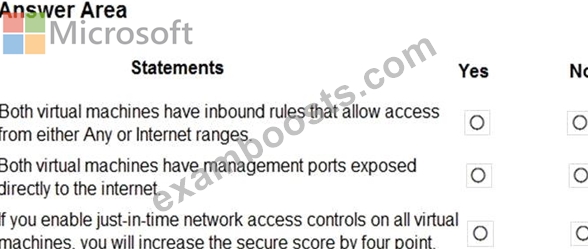
Answer:
Explanation: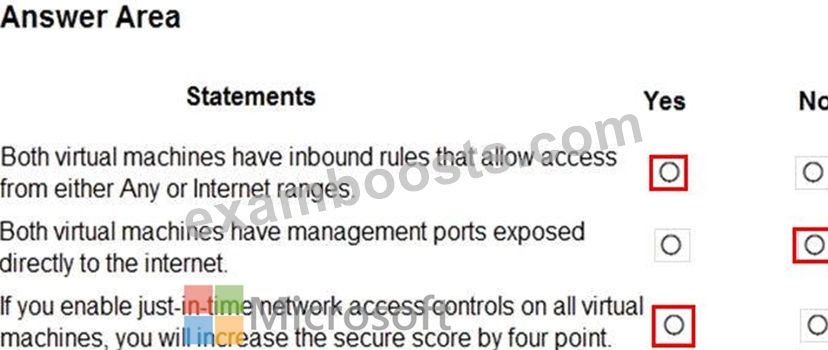
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/security-control-restrict-unauthorized-network-access/ba-p/1593833
https://techcommunity.microsoft.com/t5/azure-security-center/security-control-secure-management-ports/ba-p/1505770
NEW QUESTION # 18
You have 50 on-premises servers.
You have an Azure subscription that uses Microsoft Defender for Cloud. The Defender for Cloud deployment has Microsoft Defender for Servers and automatic provisioning enabled.
You need to configure Defender for Cloud to support the on-premises servers. The solution must meet the following requirements:
* Provide threat and vulnerability management.
* Support data collection rules.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.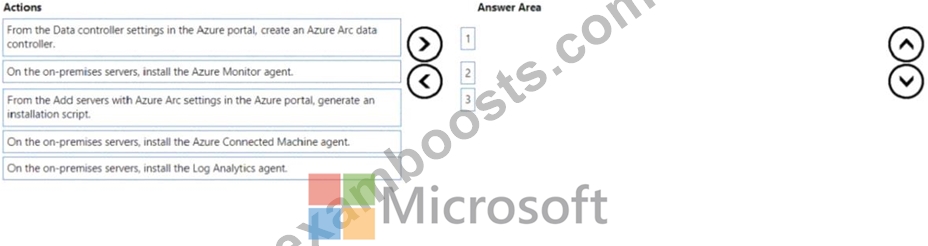
Answer:
Explanation: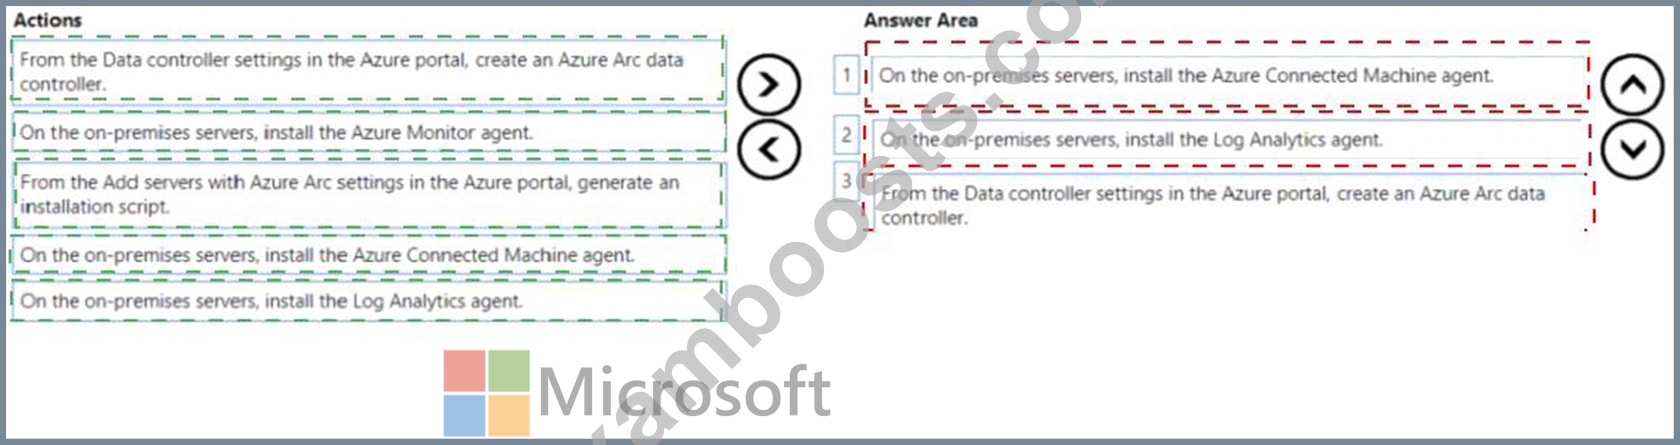
Explanation
To configure Defender for Cloud to support the on-premises servers, you should perform the following three actions in sequence:
On the on-premises servers, install the Azure Connected Machine agent.
On the on-premises servers, install the Log Analytics agent.
From the Data controller settings in the Azure portal, create an Azure Arc data controller.
Once these steps are completed, the on-premises servers will be able to communicate with the Azure Defender for Cloud deployment and will be able to support threat and vulnerability management as well as data collection rules.
Reference: https://docs.microsoft.com/en-us/azure/security-center/deploy-azure-security-center#on-premises-dep
NEW QUESTION # 19
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.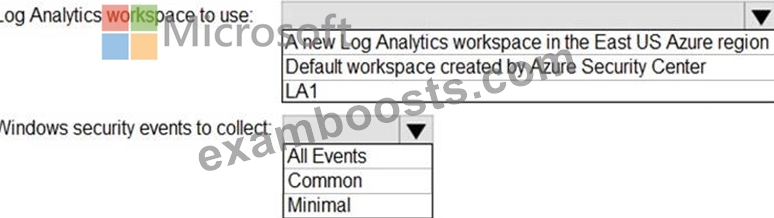
Answer:
Explanation: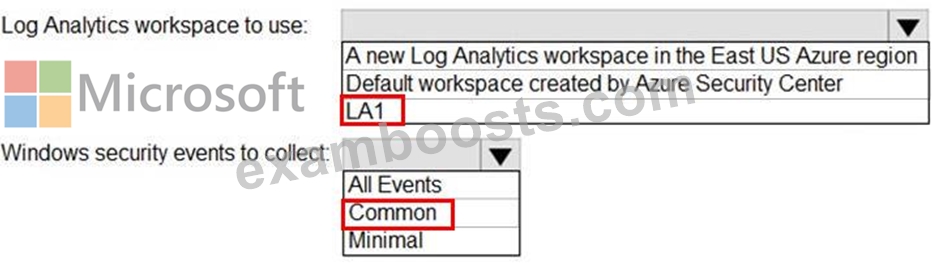
NEW QUESTION # 20
Your on-premises network contains 100 servers that run Windows Server.
You have an Azure subscription that uses Microsoft Sentinel.
You need to upload custom logs from the on-premises servers to Microsoft Sentinel.
What should you do? To answer, select the appropriate options m the answer area.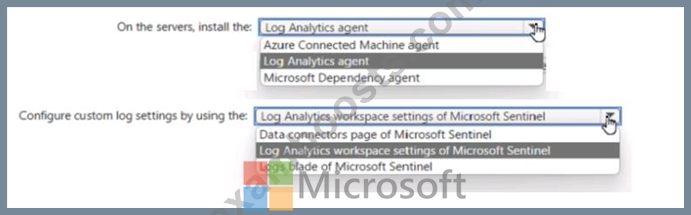
Answer:
Explanation: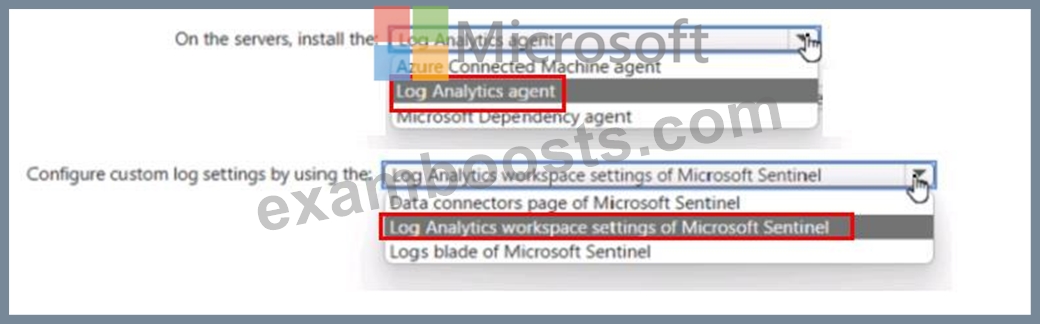
NEW QUESTION # 21
You have a custom analytics rule to detect threats in Azure Sentinel.
You discover that the analytics rule stopped running. The rule was disabled, and the rule name has a prefix of AUTO DISABLED.
What is a possible cause of the issue?
- A. The rule query takes too long to run and times out.
- B. The number of alerts exceeded 10,000 within two minutes.
- C. There are connectivity issues between the data sources and Log Analytics.
- D. Permissions to one of the data sources of the rule query were modified.
Answer: D
NEW QUESTION # 22
You have a Microsoft Sentinel workspace named sws1.
You need to create a hunting query to identify users that list storage keys of multiple Azure Storage accounts. The solution must exclude users that list storage keys for a single storage account.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.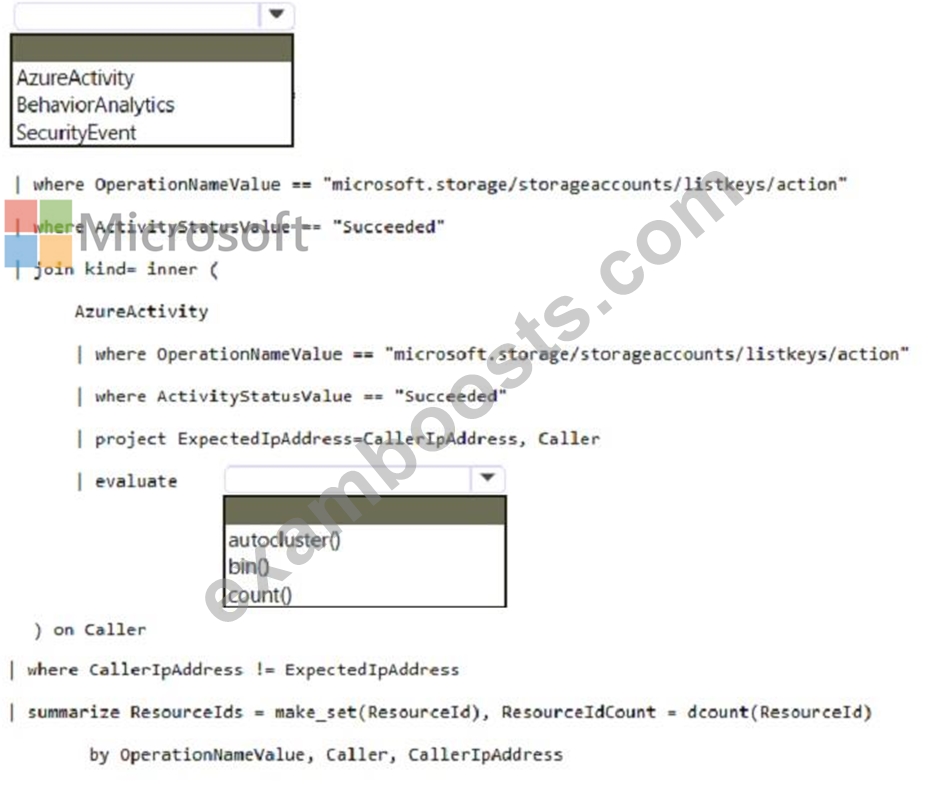
Answer:
Explanation: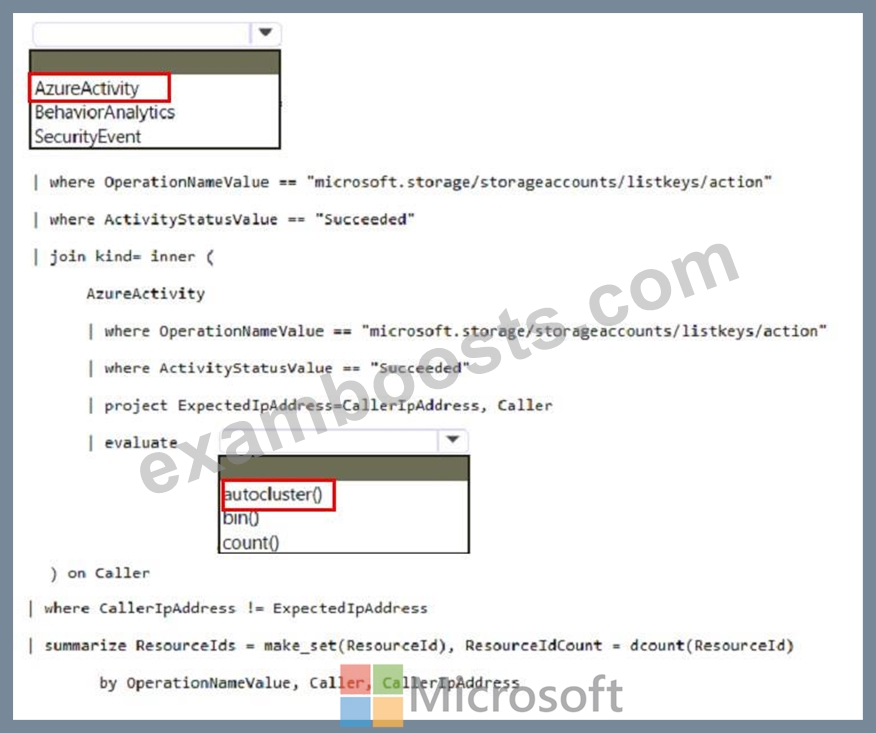
NEW QUESTION # 23
You provision Azure Sentinel for a new Azure subscription. You are configuring the Security Events connector.
While creating a new rule from a template in the connector, you decide to generate a new alert for every event. You create the following rule query.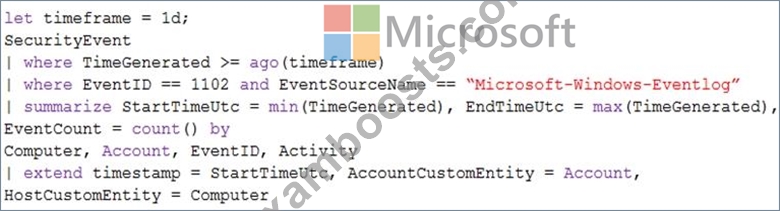
By which two components can you group alerts into incidents? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. user
- B. computer
- C. resource group
- D. IP address
Answer: A,B
NEW QUESTION # 24
You need to recommend remediation actions for the Azure Defender alerts for Fabrikam.
What should you recommend for each threat? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.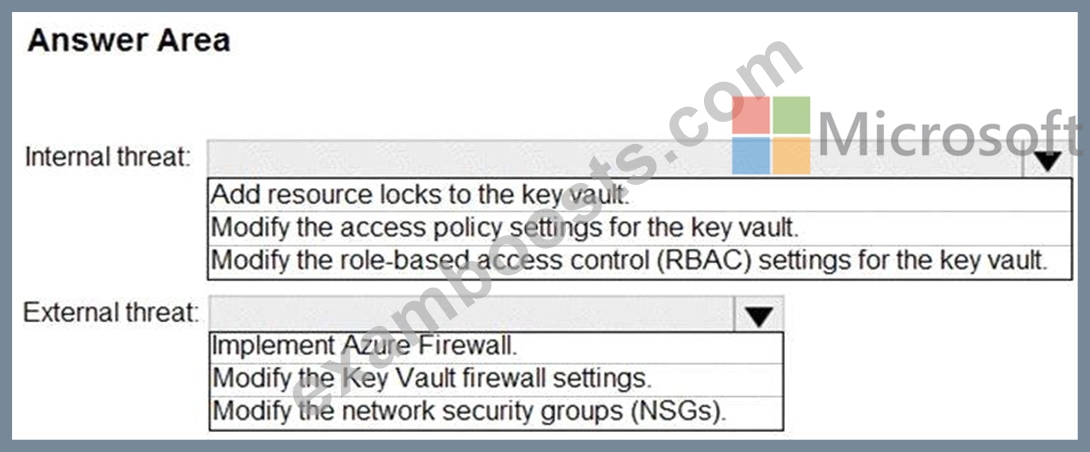
Answer:
Explanation: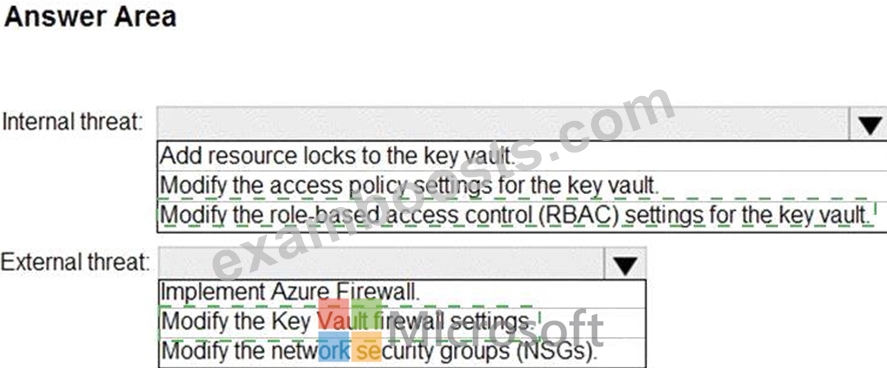
Explanation: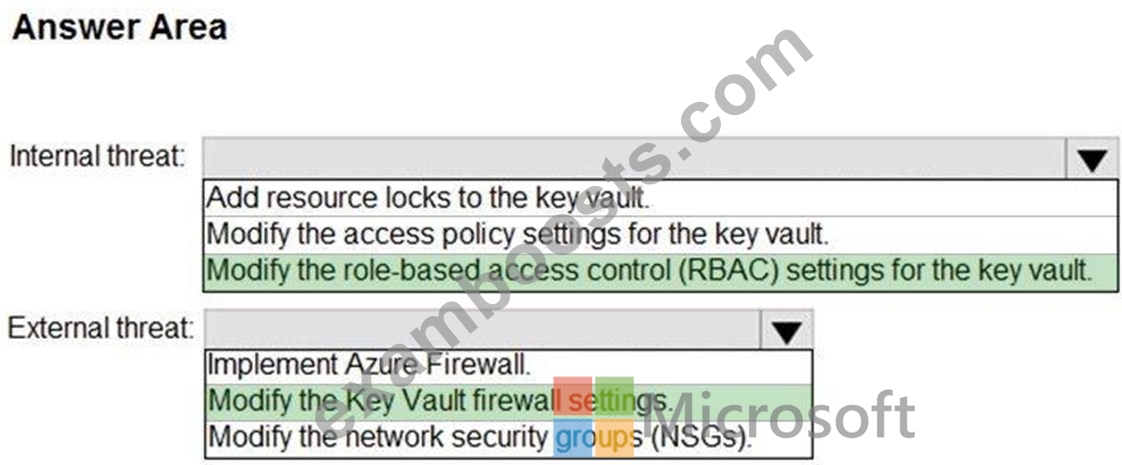
Reference:
https://docs.microsoft.com/en-us/azure/key-vault/general/secure-your-key-vault
NEW QUESTION # 25
You have a Microsoft Sentinel workspace named SW1.
In SW1, you investigate an incident that is associated with the following entities:
* Host
* IP address
* User account
* Malware name
Which entity can be labeled as an indicator of compromise (loC) directly from the incident s page?
- A. user account
- B. host
- C. malware name
- D. IP address
Answer: C
NEW QUESTION # 26
You deploy Azure Sentinel.
You need to implement connectors in Azure Sentinel to monitor Microsoft Teams and Linux virtual machines in Azure. The solution must minimize administrative effort.
Which data connector type should you use for each workload? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.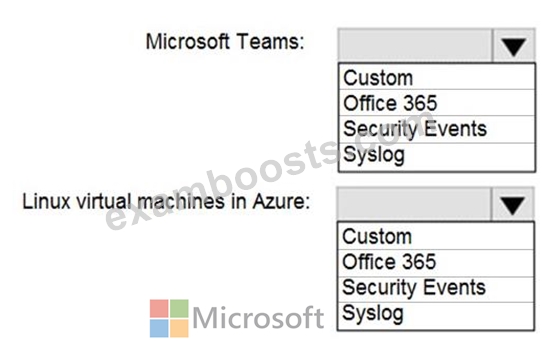
Answer:
Explanation: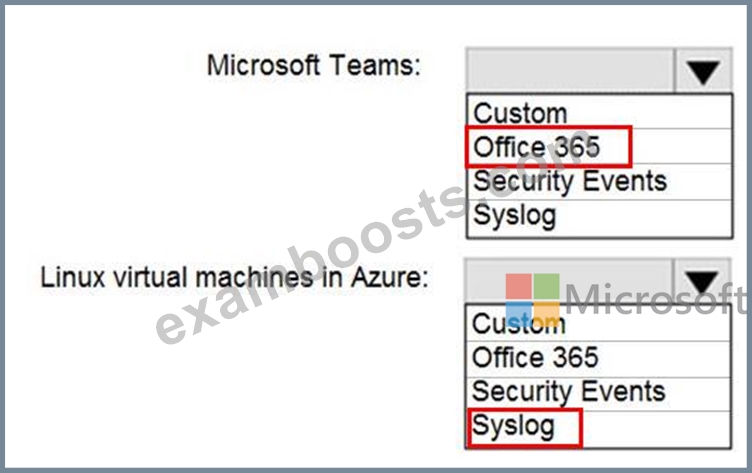
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-office-365
https://docs.microsoft.com/en-us/azure/sentinel/connect-syslog
NEW QUESTION # 27
You need to add notes to the events to meet the Azure Sentinel requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.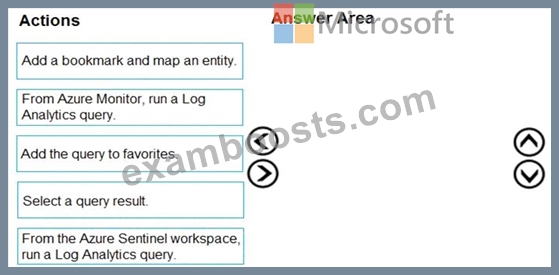
Answer:
Explanation: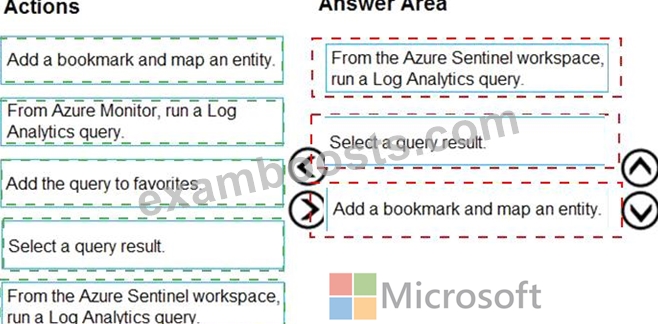
Explanation: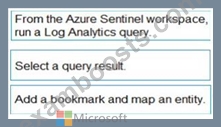
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/bookmarks
NEW QUESTION # 28
You need to restrict cloud apps running on CUENT1 to meet the Microsoft Defender for Endpoint requirements. Which two configurations should you modify? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Advanced features from the Endpoints Settings in the Microsoft 365 Defender portal
- B. Microsoft Defender for Cloud Apps anomaly detection policies
- C. the Onboarding settings from Device management in Settings in Microsoft 365 Defender portal
- D. the Cloud Discovery settings in Microsoft Defender for Cloud Apps
Answer: A,D
NEW QUESTION # 29
You have a Microsoft 365 subscription that uses Microsoft 365 Defender.
You need to identify all the entities affected by an incident.
Which tab should you use in the Microsoft 365 Defender portal?
- A. Devices
- B. Investigations
- C. Alerts
- D. Evidence and Response
Answer: D
Explanation:
The Evidence and Response tab shows all the supported events and suspicious entities in the alerts in the incident.
Reference: https://docs.microsoft.com/en-us/microsoft-365/security/defender/investigate-incidents
NEW QUESTION # 30
HOTSPOT
From Azure Sentinel, you open the Investigation pane for a high-severity incident as shown in the following exhibit.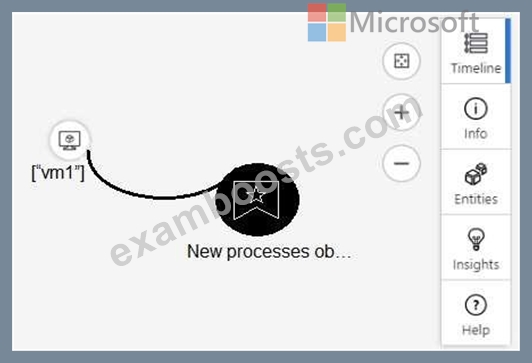
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Hot Area: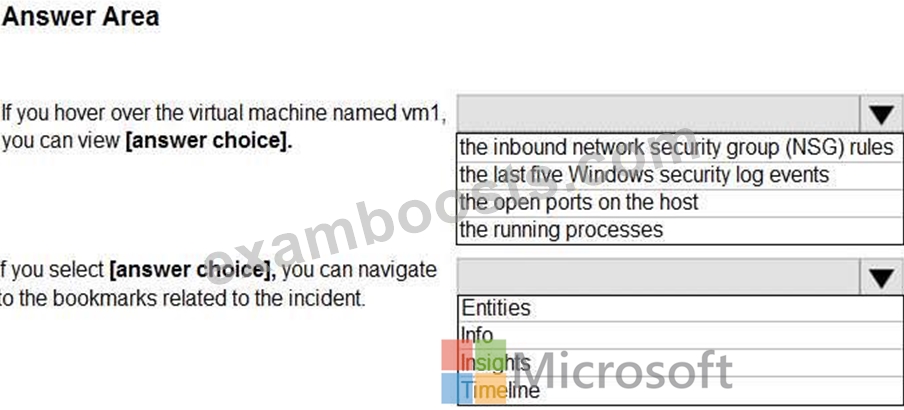
Answer:
Explanation: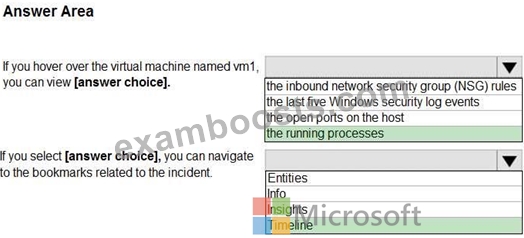
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-investigate-cases#use-the-investigation-graph-to-deep- dive
NEW QUESTION # 31
......
Verified SC-200 exam dumps Q&As with Correct 283 Questions and Answers: https://www.examboosts.com/Microsoft/SC-200-practice-exam-dumps.html
SC-200 Dumps PDF and Test Engine Exam Questions: https://drive.google.com/open?id=182BgCR2cauf00IaBZS2fCGApooO-VajA